Unpatched Systems Remain a Business Risk as Vcs Reports Rising Vulnerability Disclosures

What Readers Should Know
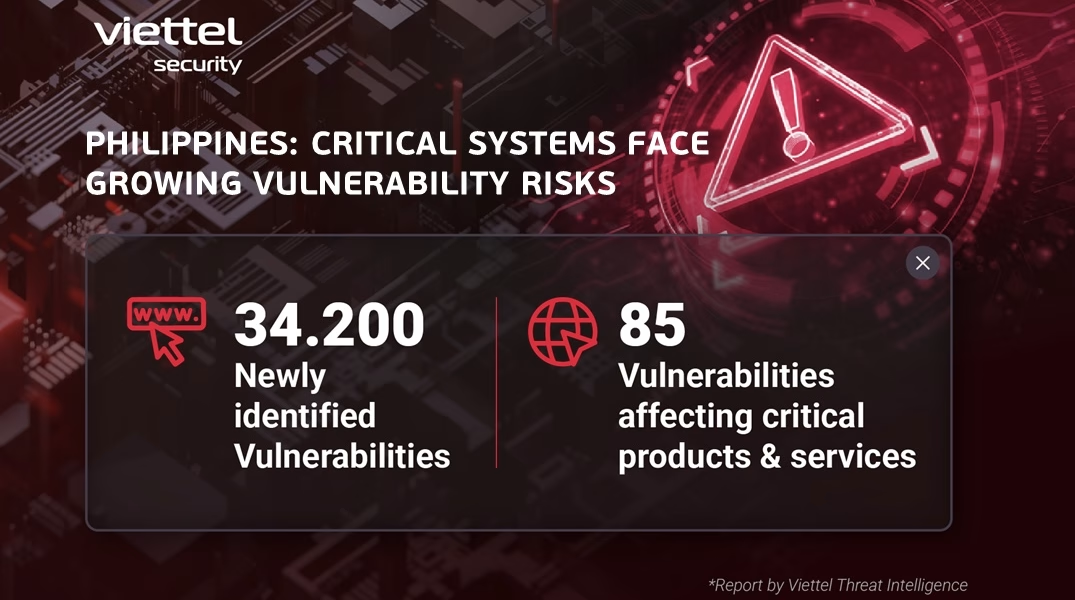
VCS reports rising global vulnerability disclosures while warning that older unpatched systems remain exposed. Its Philippine assessment identifies 85 vulnerabilities with significant potential local impact.
Key Takeaways
- VCS reports 34,223 global disclosures in Q3.
- Disclosures are not the same as successful attacks.
- Its local assessment identifies 85 relevant vulnerabilities.
- Older software weaknesses remain a concern.
- Supply-chain security complements patch management.
Viettel Cyber Security is urging Philippine businesses to prioritize unresolved software weaknesses, warning that attackers continue exploiting older vulnerabilities even as newly disclosed flaws increase.
Q3 2026 Cyber Threat Landscape in the Philippines announcement reports 34,223 newly disclosed vulnerabilities globally, compared with 9,277 in the same quarter of 2025.
That global disclosure count should not be confused with the number of Philippine breaches or successful attacks.
Local exposure requires a more specific assessment
Viettel Threat Intelligence identified 85 vulnerabilities with significant potential impact on Philippine organizations:
| Severity | Number assessed |
|---|---|
| Critical | 1 |
| High | 20 |
| Medium | 64 |
| Total | 85 |
The company says actual exploitation did not rise at the same pace as disclosures. Instead, attackers continued targeting known weaknesses in widely used enterprise systems.
VCS Country Manager Thomas Luu emphasized that identifying flaws is only part of the task; organizations must also resolve those that threaten their operations.
Trusted software can carry risk
The release also highlights software supply-chain attacks, in which compromised packages, developer accounts, or distribution channels introduce malicious code.
VCS reports that malicious packages in ecosystems such as npm and PyPI sought sensitive information, including credentials and authentication tokens.
This makes supplier oversight and software-component visibility relevant alongside patching a company’s own servers.
Make remediation part of routine operations
The company recommends maintaining asset inventories, prioritizing vulnerabilities with active exploitation, strengthening privileged access, and preparing incident-response and backup arrangements.
CISA likewise encourages organizations to use evidence of exploitation when prioritizing remediation. content.govdelivery.com
For businesses, the practical goal is a repeatable process: identify affected assets, assign responsibility, apply appropriate fixes, and verify completion.
Frequently Asked Questions
Does 34,223 represent Philippine breaches?
No. It is the reported global vulnerability-disclosure count.
How many vulnerabilities were assessed for significant local impact?
Eighty-five.
Does finding a vulnerability mean it was exploited?
No. Disclosure and exploitation are different.
What is a software supply-chain risk?
A compromise introduced through trusted software components or delivery channels.
What does VCS recommend prioritizing?
Relevant exposed systems and vulnerabilities with known active exploitation.


Gabriel
Introvert, wanderer, blogger, foodie, a hip-hop music writer, and one of the co-founders of a tech start-up company called GigsManila.
Related Articles
More by category, author, or tags
Sophos Adds AI Service Controls and Coordinated Network Defense Tools
Add as a preferredsource on GoogleFind this story on GoogleSophos Adds AI Service Controls and Coordinated Network Defense Toolsgoogle.com · Opens in...

Keeper Introduces Self-Hosted Access Security for Disconnected Networks
Add as a preferredsource on GoogleFind this story on GoogleKeeper Introduces Self-Hosted Access Security for Disconnected Networksgoogle.com · Opens in a new...

Converge Earns Iso/Iec 27001:2022 Certification for Information Security Management
Add as a preferredsource on GoogleFind this story on GoogleConverge Earns Iso/Iec 27001:2022 Certification for Information Security Managementgoogle.com · Opens in a...

Keeper Security Adds On-Device AI Phishing Warnings to Its Browser Extension
Add as a preferredsource on GoogleFind this story on GoogleKeeper Security Adds On-Device AI Phishing Warnings to Its Browser Extensiongoogle.com · Opens...

Tenable Expands Security Ecosystem with Open for AI Partner Workflows
Add as a preferredsource on GoogleFind this story on GoogleTenable Expands Security Ecosystem with Open for AI Partner Workflowsgoogle.com · Opens in...

Keeper Security and Tenable Integrate Cloud Risk Remediation and Scan Credential Management
Add as a preferredsource on GoogleFind this story on GoogleKeeper Security and Tenable Integrate Cloud Risk Remediation and Scan Credential Managementgoogle.com ·...